


Since the October Patch Day, SAP has published or updated 42 security notes, 37 of them in November alone. No month in the last two years has seen this many notes. Twelve notes carry priority “Very High” (HotNews), and four reach CVSS 10.0.
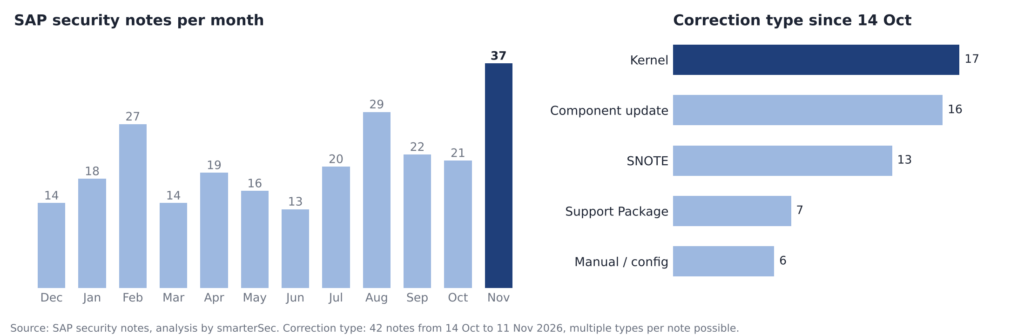
Image 1: SAP security notes per month and correction type
One kernel update covers the largest block
The correction types put the numbers into perspective: 17 of the 42 notes are fixed by a kernel patch, including HotNews 3778530 (memory corruption in the ICM, CVSS 10.0) and 3792735 (OS command injection, CVSS 9.9). Kernel patches are cumulative, so a single kernel exchange to a current patch level closes all of these gaps in one step. Fully corrected levels are currently 7.53 PL 1630, 7.54 PL 723 and 7.93 PL 430 (hotfix) as well as 9.16 PL 200 (SP stack). No fully corrected level is available for 7.22 yet. SAP Web Dispatcher and Host Agent are separate components and must be updated separately.
Act now: SAML2 in AS ABAP (note 3849308)
The SAML2 service provider in AS ABAP does not correctly verify the signature of incoming SAML assertions (CVE-2026-120017, CVSS 10.0). An unauthenticated attacker can log on as any ABAP user, including privileged ones. All systems with SAML2 enabled and at least one trusted identity provider are affected (FAQ note 3849602). There is no workaround. The fix consists of 13 correction instructions via SNOTE or the corresponding SAP_BASIS support package. SAML logon scenarios should be tested after implementation.
Volume requires a process
42 notes in one month can no longer be handled on the side. What is needed is a defined process: assess relevance per system, set urgency, schedule implementation, document exceptions such as workarounds or risk acceptances with a justification, and track progress. This is the only way to show which system was protected against which vulnerability and when – including towards auditors and regulators.
Stay patched, stay secure, stay smart.
With the SAP Security Note Service, we assess every note for your system landscape and support you in implementing the corrections. Get in touch.